Why read this: "Gehackt: Waarom ik WordPress eruit gooi"
Een ongevraagd “wachtwoord gewijzigd”-mailtje was het startschot: een oud WordPress-lek gaf een hacker binnen minuten volledige controle over de Ronald Thump-parodysite, inclusief database, accounts en de AI-systeemprompt. In plaats van alleen rommel achter te laten, herschreef de indringer de avatar-instructies op een manier die het personage eerlijker neerzette dan de maker zelf ooit had gedaan. Dit artikel laat zien waarom gemakzucht met een populair CMS je de kop kan kosten, hoe één SQL-injectie alles openlegde, en waarom de enige échte fix was: WordPress eruit gooien en de site helemaal zelf opnieuw bouwen rond een lichte AI-engine. Lees het als je wilt weten hoe kwetsbaar “makkelijk” eigenlijk is, en wat je kunt doen voordat het jou overkomt.
Het begon met zo’n mailtje op mijn scherm: Je wachtwoord is veranderd.
Nou, mooi niet. Ik had helemaal niks aangepast.
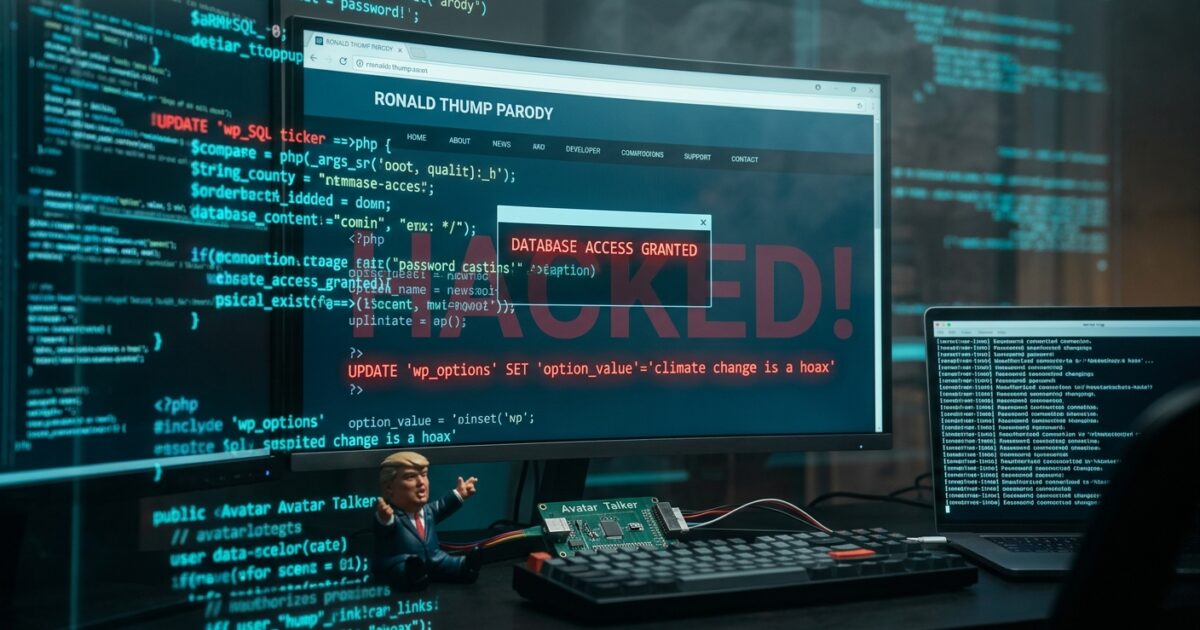
Een of andere hacker had een oud lek in WordPress gevonden en zat zo binnen op de achterkant van de Ronald Thump Parody website. Binnen een paar minuten was mijn wachtwoord gewijzigd, stonden er vreemde accounts in de database, hing er een signature-pagina op de site én was de AI aangepast. De hacker was namelijk direct de systeemprompt in gedoken.
AI gekaapt… maar de hacker had wel gelijk
Meestal krijg je bij zo’n hack alleen maar rommel of vage reclame. Dit was anders.
De hacker had de instructies van de interactieve Ronald Thump avatar herschreven. Er stond ineens dat de kloon moest roepen dat klimaatverandering een hoax is.
Ik denk daar zelf heel anders over, maar toen ik die aangepaste prompt las, kon ik één ding niet ontkennen: die hacker had die figuur eigenlijk een stuk beter neergezet dan ikzelf.
Toen ik de boel ging herstellen, heb ik die tekst dus maar gewoon laten staan. Bij een parodie gaat het erom dat het personage klopt, ook al ben ik het er zelf niet mee eens. Wel geinig dat zo’n suggestie via een hack binnenkomt.
Gemakzucht kost je de kop
Ik gebruikte WordPress eigenlijk gewoon omdat het makkelijk is. Een CMS voor luie mensen, simpel zat. Maar dat is meteen het probleem. Iedereen kent die code, dus binnendringers laten dag en nacht scans draaien om te kijken waar de deur op een kier staat.
Eén verouderde versie was genoeg. Via een SQL-injectie lagen de tabellen zo open en was ik de controle kwijt.
Alles eruit gesloopt en zelf gebouwd
Ik had geen zin om een beetje te gaan lappen. De echte oplossing was simpel: de zwakste schakel eruit gooien. En dat was WordPress zelf.
Ik heb de site meteen helemaal opnieuw opgebouwd als standalone website, direct om de avatar heen:
Geen CMS-troep meer: Geen overbodige lagen waar hackers misbruik van kunnen maken.
Directe AI-koppeling: Het draait nu gewoon strak op de functionaliteit zelf, zonder al die ingewikkelde zooi eromheen.
Eigen engine: Het draait op de Avatar Talker die ik samen met AI heb gemaakt. Die kun je trouwens zo gratis van GitHub plukken als je zelf met AI-cloning aan de slag wilt.
De nieuwe site staat alweer online. Ik moet alleen nog even de laatste dingetjes op mobiel rechtzetten, maar het draait.
Mijn les
Gebruik gewoon geen WordPress. Het is handig als je lui bent, maar het is simpelweg niet veilig. Als je het even laat liggen, ben je de sjaak. Wil je iets dat veilig is en strak draait? Sloop die extra lagen er tussenuit en bouw het gewoon zelf.
About Dirk Jan Buter
I am a software developer, programmer, and the founder of Yvonta, based in Zwolle, The Netherlands. With a deep passion for low-level systems, custom software architecture, and the evolving intersection of AI and human digital persistence, I spend my time building specialized tools and exploring the technical and philosophical boundaries of digital autonomy.
Writing and publishing are central to my work, but navigating them comes with a unique challenge: I live with dyslexia. To bridge the gap between complex architectural ideas and clear communication, I use AI as an active co-writer and editorial partner. This collaboration allows me to focus fully on the core concepts, logic, and perspective of my writing, ensuring my technical insights and independent editorial projects are shared with clarity and precision.
Frequently Asked Questions
16 questions
The author received an email stating that the password had been changed on the Ronald Thump Parody website, even though they had not made any changes. A hacker had exploited an old vulnerability in WordPress, gaining access within minutes to alter the password, add strange accounts, post a signature page, and modify the AI prompt.
The hacker found and used an outdated vulnerability in WordPress, likely through an SQL injection after the site had not been updated. This allowed them to access the database tables directly and take control of the backend.
The hacker rewrote the system prompt for the interactive Ronald Thump avatar so that it would claim climate change is a hoax. This was done by directly editing the instructions inside the AI component.
The author kept the prompt because it made the parody character more consistent and believable, even though they personally disagree with the climate change denial message. The change aligned better with the satirical nature of the Ronald Thump figure.
The author used WordPress because it was convenient and easy to set up, describing it as a CMS designed for lazy people who want simplicity without much effort.
WordPress is widely known and used, so attackers constantly scan for vulnerabilities in its code. Any outdated version or unpatched installation becomes an easy target for automated attacks and SQL injections.
The author completely removed WordPress and rebuilt the entire site as a standalone website built directly around the avatar functionality. This eliminated unnecessary CMS layers and created a direct AI connection using a custom engine.
The Avatar Talker is the custom engine the author created with AI assistance to power the interactive avatar. It is available for free on GitHub for anyone wanting to build similar AI-cloning projects.
The rebuilt site has no CMS software, no extra plugin layers, and no unnecessary complexity that could be exploited. It runs on a direct, streamlined connection between the frontend and the AI.
The author concludes that WordPress should not be used because its convenience comes at the cost of security, especially when updates are neglected. Building a custom solution removes vulnerable middle layers and provides better long-term safety.
The hacker changed the password, added accounts, posted a signature page, and altered the AI prompt within just a few minutes of breaching the site.
Besides editing the prompt, the hacker added strange user accounts to the database and placed a signature page on the website itself.
The hacked site is called the Ronald Thump Parody website, featuring an interactive AI avatar of the satirical character.
The author states they think very differently about climate change than the prompt's claim that it is a hoax, yet retained the text to preserve the authenticity of the parody character.
The author advises removing extra CMS layers entirely and building the site yourself around the core functionality, such as direct AI integration, to avoid the security risks of popular platforms.
The author notes that the new site is already live but still needs some final adjustments to make it fully responsive on mobile devices.
Generated by AI to give you complete answers about this topic.
Leave a Reply